3rdComply is changing its mission. The original goal, killing the security questionnaire, still
stands. But it turned out to be too small.
Where 3rdComply Started
When 3rdComply launched, the idea was simple: replace the security questionnaire. The
spreadsheet vendors dread, risk teams chase for weeks, and nobody really questions
once it’s filled in.
That is still part of the plan. But after many conversations with TPRM teams across EMEA
and APAC, 3rdComply founder Ferry came to a clear conclusion. Fixing the questionnaire
fixes how vendors get assessed. It doesn’t fix which vendors get assessed at all.
The Real Problem: Most Vendors Are Never Checked
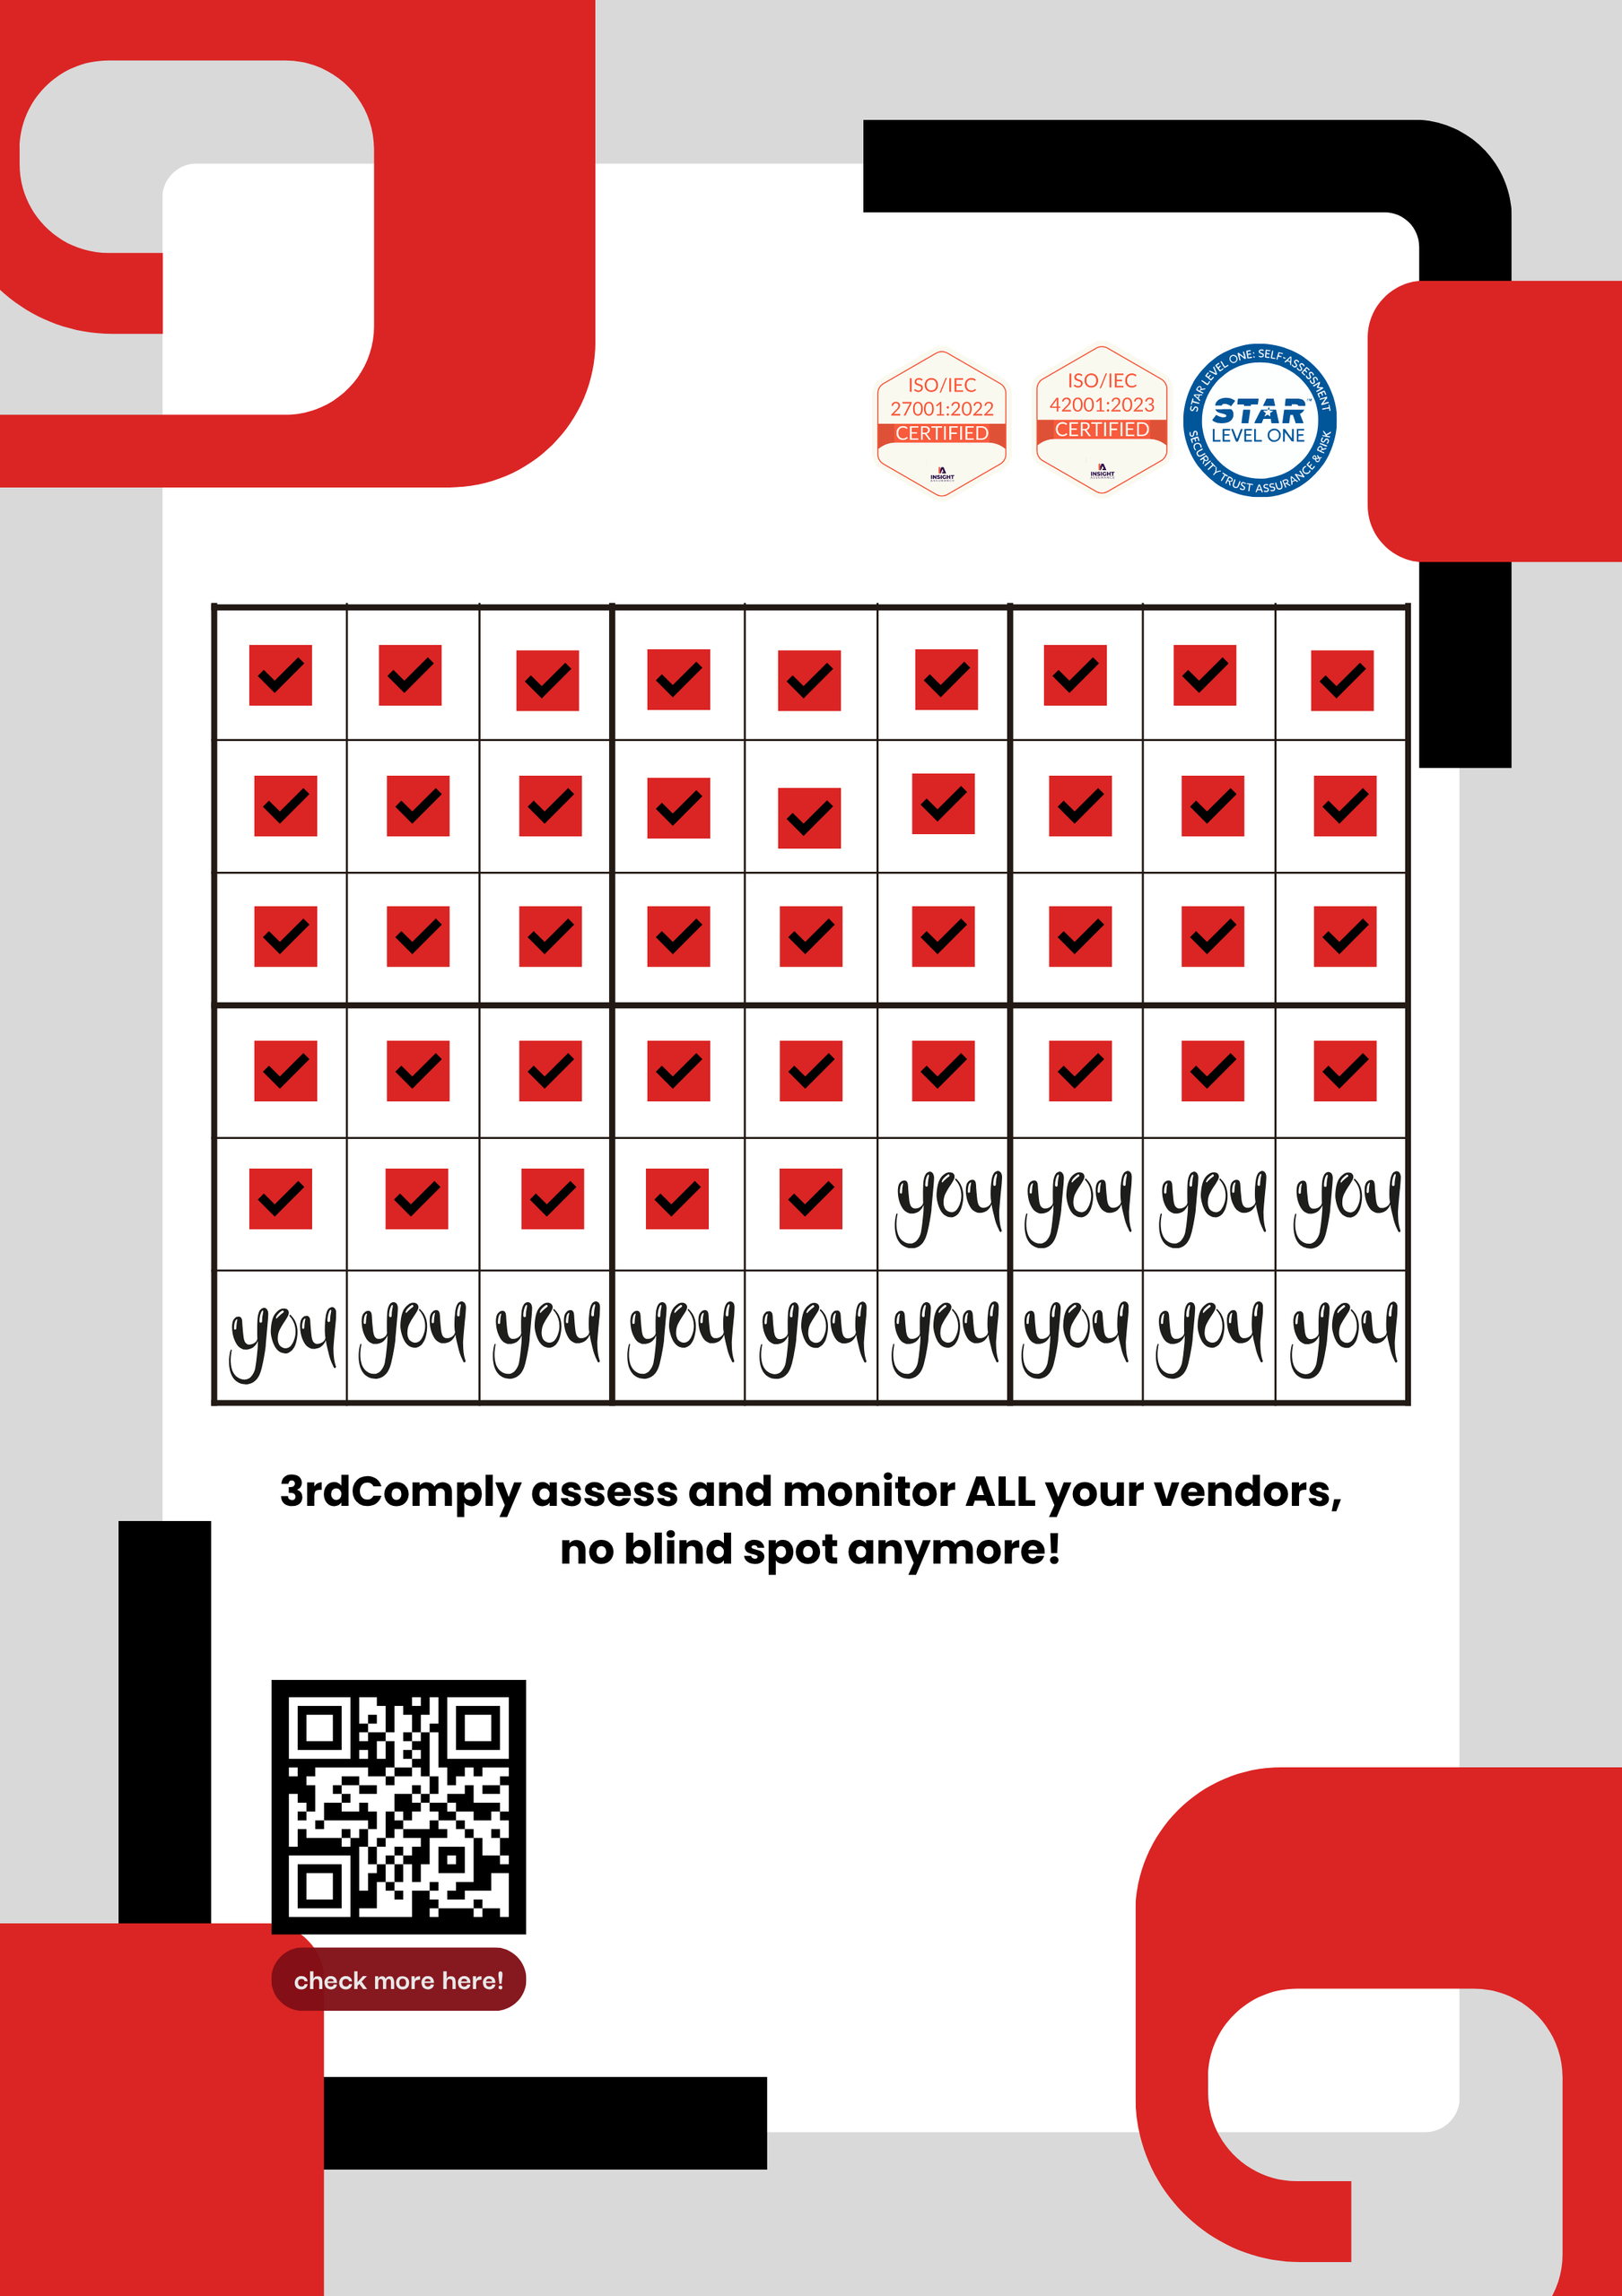
In most companies, only 5 to 10% of vendors ever get a proper security assessment. The
rest are labelled “low risk” or pushed to next year.
The reason isn’t bad intent. A single assessment takes 2 to 4 weeks, and a large company
can have more than 1,000 suppliers. No TPRM team has the hours to cover all of them, so
they cover the top tier and hope for the best. Even the vendors that do get checked are
usually reviewed once a year.
That creates a blind spot with a policy written around it. And regulations like NIS2 and
DORA don’t accept “we only looked at the important ones” as an answer. Neither do
attackers, who often come in through the supplier nobody was watching.
The New Mission: No More Blind Spots
Every company working with 3rdComply, on the platform or through the managed service,
should be able to see its whole supply chain. Not just the top tier.
If a company has 800 vendors, 3rdComply assesses and monitors all 800. If it has 6,000, all
6,000.
What That Means In Practice
Covering every vendor only works if each assessment takes hours instead of weeks. That
is what the 3rdComply platform is built for:
- AI vendor assessment that reviews vendor documentation and maps findings to frameworks like ISO 27001, SOC 2, NIS2 and DORA
- Continuous monitoring instead of a once-a-year snapshot, including security posture scanning and 4th party monitoring
- Shadow vendor detection to find the third parties that never made it onto the vendor list
- Your own methodology, so assessments follow the company’s risk approach and leave an auditable trail per vendor
Companies can run it themselves on the platform, or let the 3rdComply team handle the
work as a managed service.
Too Ambitious?
Maybe. Full coverage of every vendor is not how TPRM has worked so far. But the tools to
do it now exist, and the regulatory pressure to do it is only growing. 3rdComply would
rather aim for the whole supply chain and get close than settle for the top 10%. 3rdComply.com